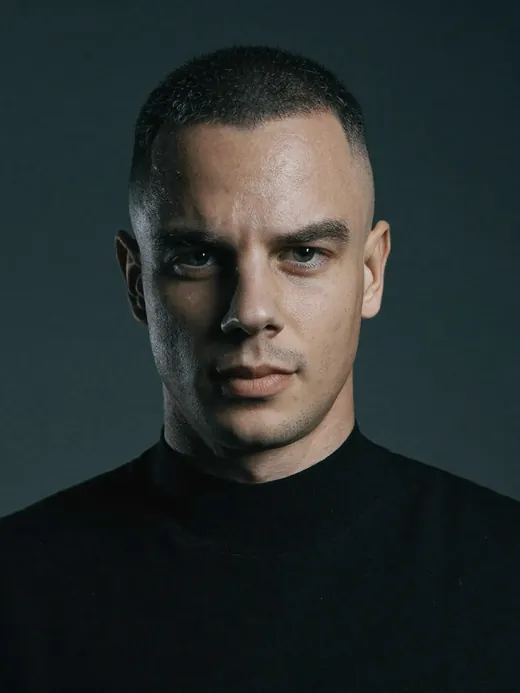
Vlad Kraevsky
Penetration tester and cybersecurity team lead. Since 2019 I have run 170+ penetration tests for 80+ companies and worked on the security of many Ukrainian banks, as well as government bodies and law enforcement. I founded Veiltrack so that growing companies get the same level of testing.
I look at a company the way an attacker would
I check what the internet shows about a company, how staff react to suspicious emails, who can reach email and the cloud, and whether one account can get to someone else's data.
After the test I explain in plain words what we found, what it could cost the business and what to fix first. I write the report so that both the IT team and the owner can work with it.
At Veiltrack I lead every project from the first call to the retest and answer for the result.
170+ penetration tests for 80+ companies since 2019
Banks, payment systems, the public sector and products where a mistake is expensive. I never name clients: all work is under NDA.
- 2024-2026 · Cybersecurity team lead in the financial sector: banks, crypto exchanges, e-commerce
- 2022-2024 · Security Engineer: building security for a SaaS product from scratch (under NDA)
- 2021-2023 · Projects for the public sector and law enforcement: audits, open-source and dark-web intelligence, physical security (under NDA)
- 2019-2021 · Penetration tester: banks and payment systems, consulting firm (under NDA)
What I test
- Web applications, APIs and external infrastructure
- How staff react to realistic phishing
- Accounts, access and cloud: Microsoft 365, Google Workspace
- What a company exposes on the internet
Ground rules
- An NDA before any work starts
- Active testing only with written permission
- A report your team can act on the next day
- A retest after the fixes
I break down real attacks in plain words
What happened, what it means for a company and what to check in yours.
Want an independent look at your company's security?
30 minutes online: I will tell you what to check first and how long it takes. We never touch your systems without written permission.