What is a penetration test, in plain words?
What a penetration test is: definition, why companies do it, how it differs from a scan and a red team, stages, types, report, timing, written permission.
We explain how security testing works: scope, price, report and retest. No scare tactics, with links to sources.
What a penetration test is: definition, why companies do it, how it differs from a scan and a red team, stages, types, report, timing, written permission.
What a website and API security test covers: OWASP risks in plain words, what to prepare, what is out of scope and what report you get. Table, checklist.
Who we are, who tests, which standards, how we store data, what is in the report, prices and payment, what we do not do. Short answers for due diligence.
When a SaaS startup needs a pentest, what SOC 2 and ISO 27001 mean, what a customer's security questionnaire asks and what to show. Table and checklist.
How a red team differs from a pentest: goal, scope, duration, who knows about it, what you learn. A table, a decision rule and a readiness checklist.
Phishing simulation providers in Ukraine, running one legally and without shaming, scenarios by difficulty, metrics, questions for a provider, how often.
How to vet a pentest provider: 46 questions on the team, methodology, data, report, retest and contract, what a good answer looks like, how to score. PDF.
What a mobile app pentest checks: data on the phone, the API, login and sessions, payments, secrets in code, the backend. Based on OWASP MASVS and MASTG.
What an internal network and Active Directory pentest shows: extra admins, shared passwords, legacy protocols, flat network. What to provide, what you get.
A free cybersecurity checklist: 15 items on accounts, email, devices, backups, the website, people and incidents, how to verify each one, and a PDF.
What attackers target in fintech and payments, what the NBU and PCI DSS require, what to check in APIs and transfer logic. A threat table and checklist.
Cloud penetration testing and AWS, Azure, GCP security audits: IAM, public buckets, keys, network, logs, Kubernetes, CI/CD and each provider’s rules.
Four ways to check company security without a security person: self-check, external assessment, pentest, program. Table, a 2-hour plan and a checklist.
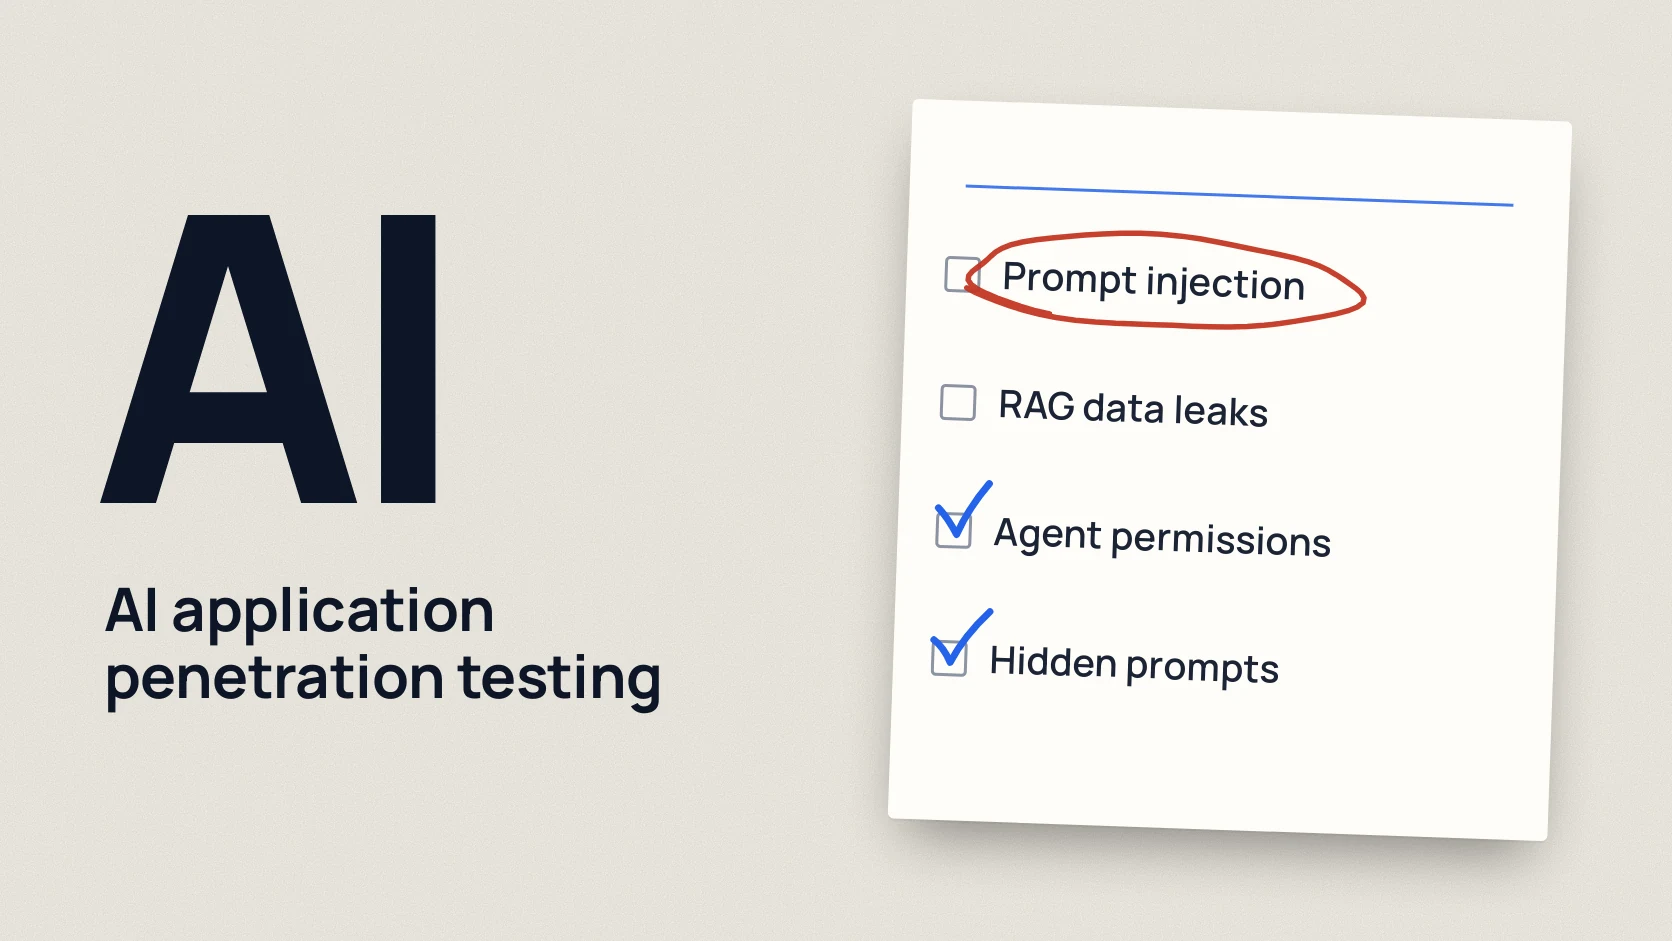
What an AI application pentest checks: prompt injection, RAG data leaks, agent permissions, hidden prompts, cost abuse. Based on the OWASP LLM Top 10 2026.
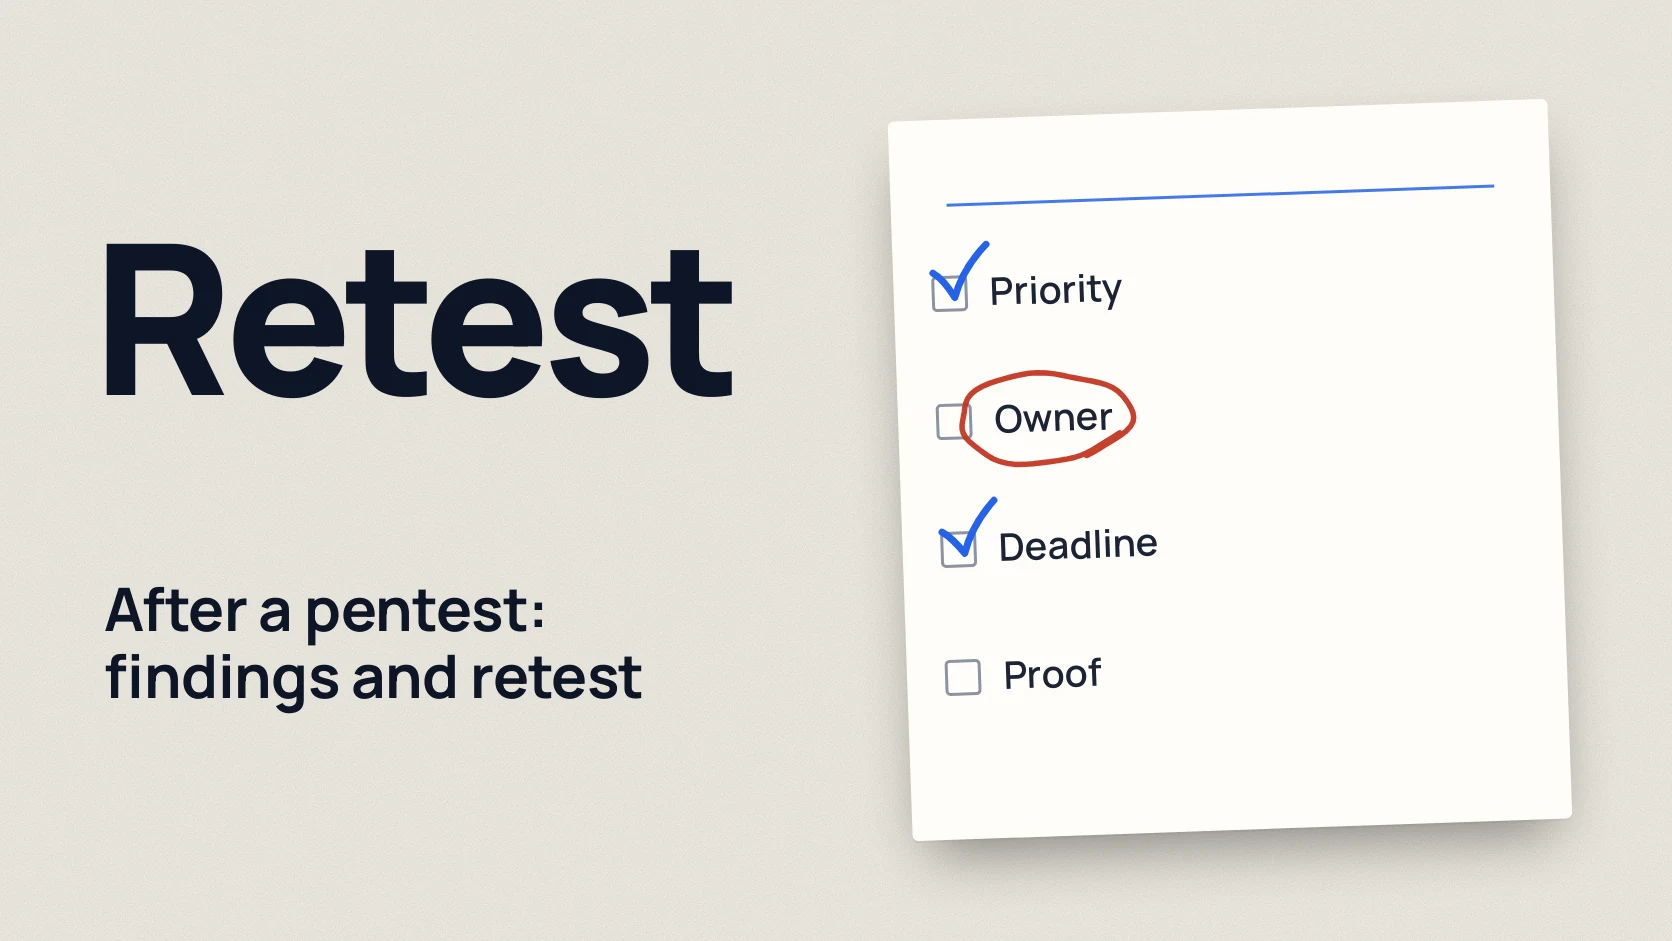
What to do with a pentest report: reading CVSS, setting priorities, who owns each finding, a remediation plan and what a retest proves. With a checklist.
The first 10 security steps for a company with no security person: why each matters, how to check it in 15 minutes and who owns it. Table and checklist.
PHP2Shell: which PHP versions are fixed, how to find the version your live site runs, what to check in WordPress, admin accounts and backups. A checklist.
Six Microsoft 365 security checks in an hour: MFA, legacy sign-in, admins, mail forwarding, file sharing, logs. Where to click and what the result means.
How to prepare for a pentest: scope, test accounts, permission, cloud and hosting rules, backups, the report and the retest. A client checklist.
SPF, DKIM and DMARC in plain words, external sender tags, link protection, a bank detail rule for accounting and phishing simulations without shaming.
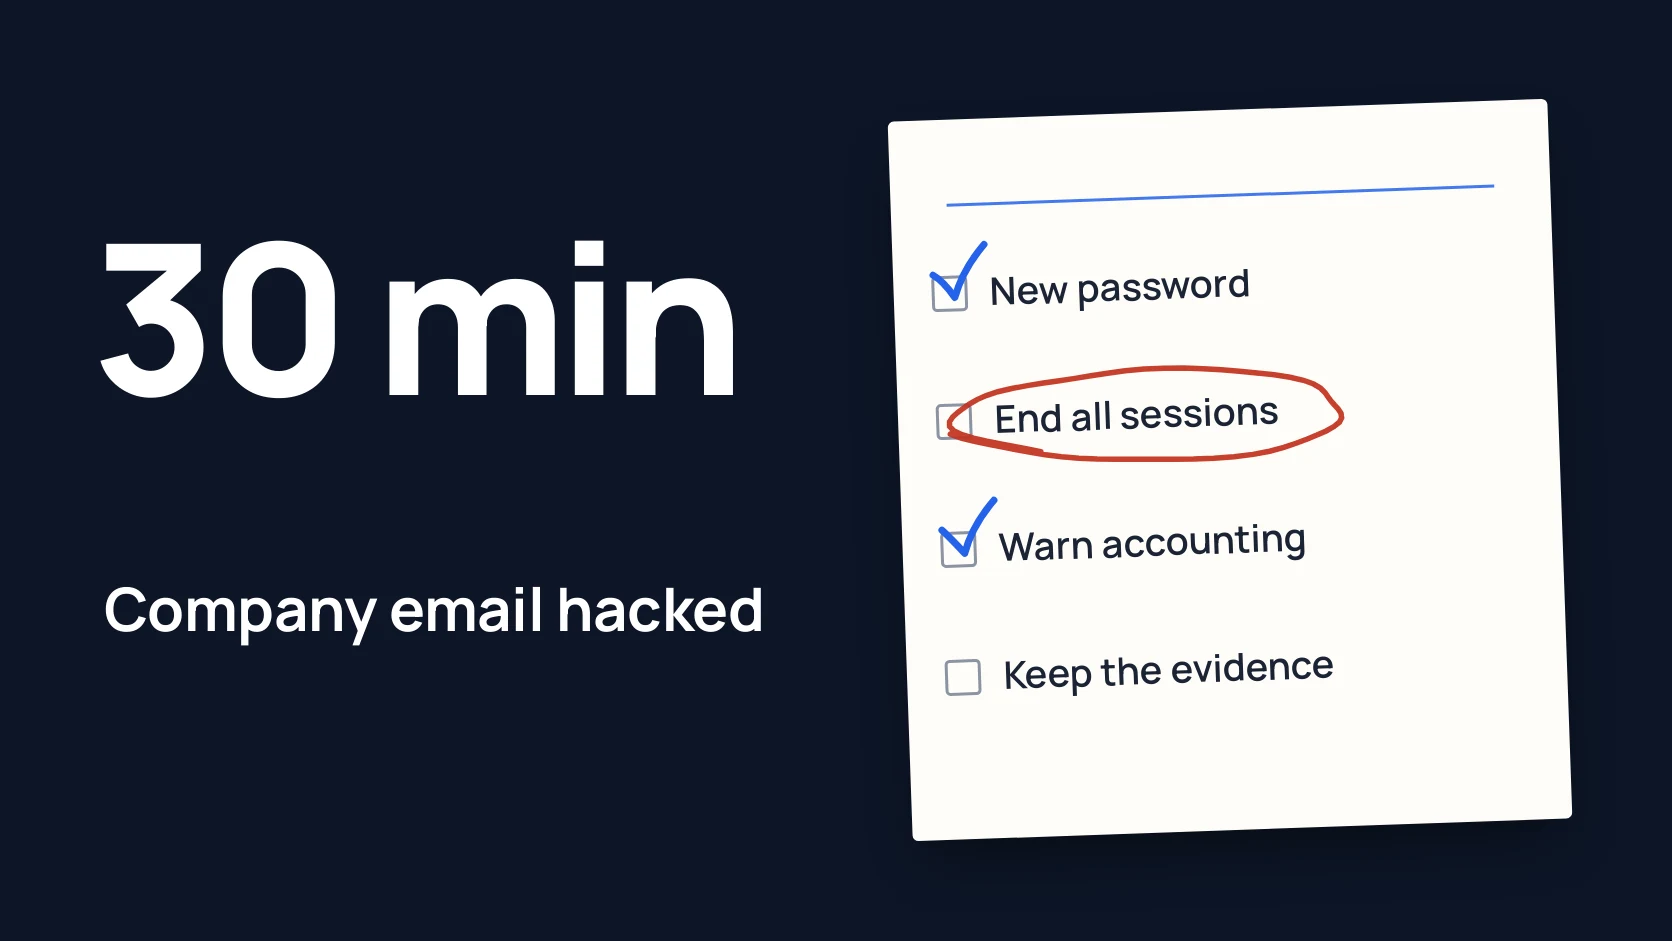
A step by step plan for the first 30 minutes after a company email or account is hacked: stop the damage, warn accounts, keep evidence, who to call.
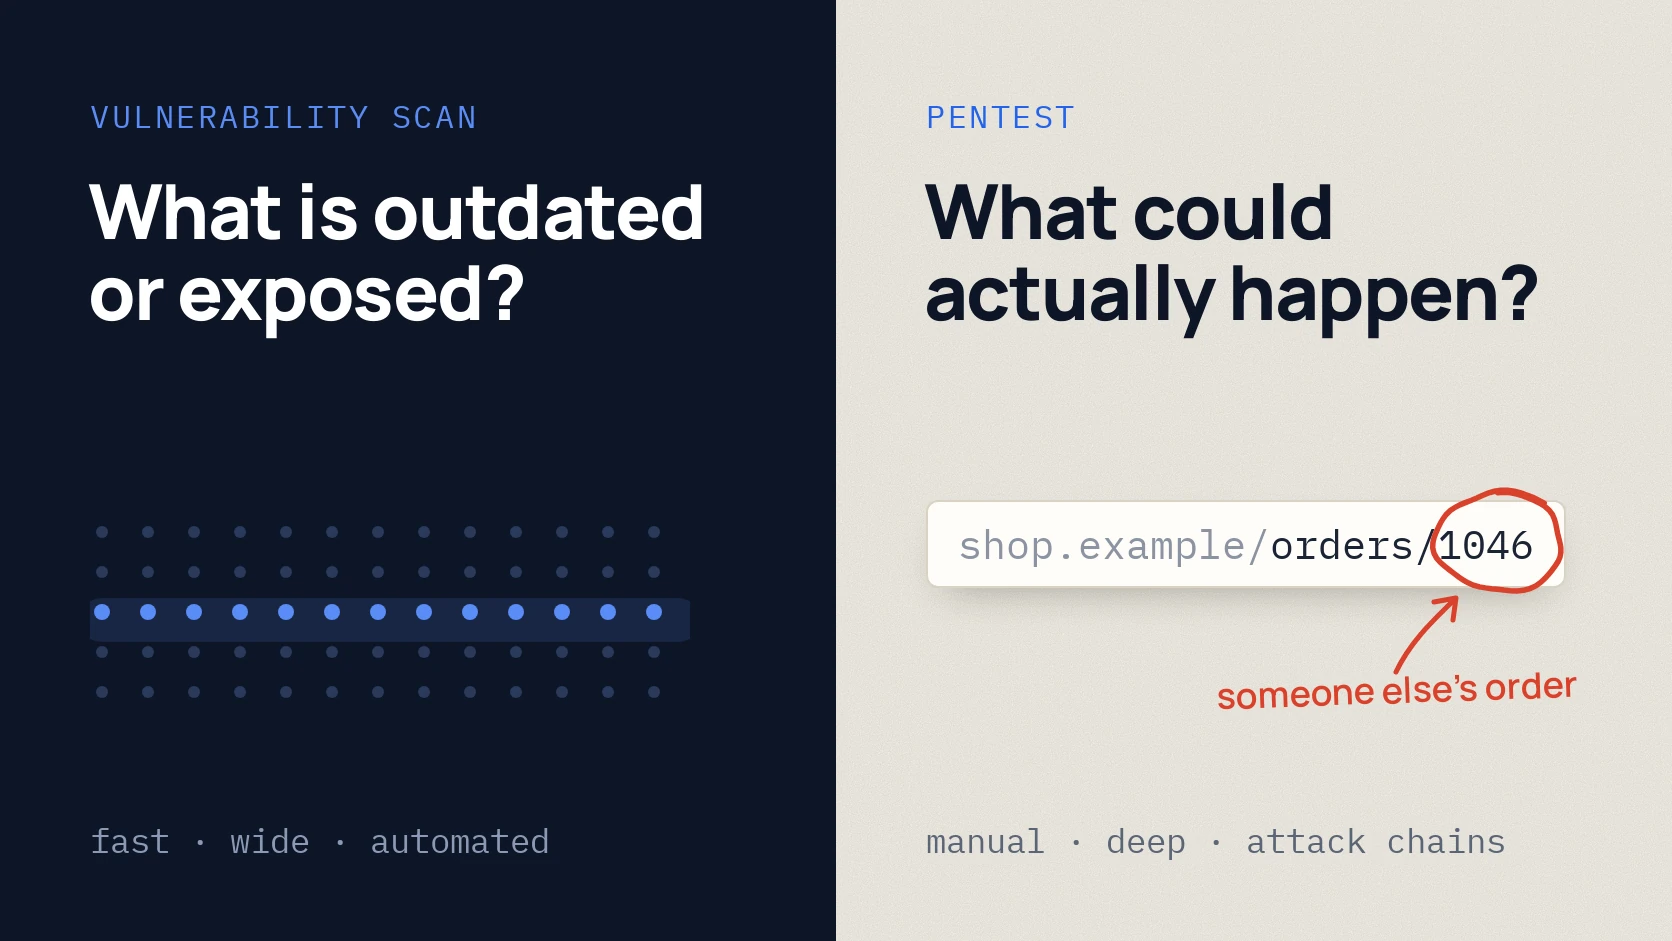
How a pentest differs from a vulnerability scan: what each finds and misses, how long it takes and when to choose which. Table and checklist.
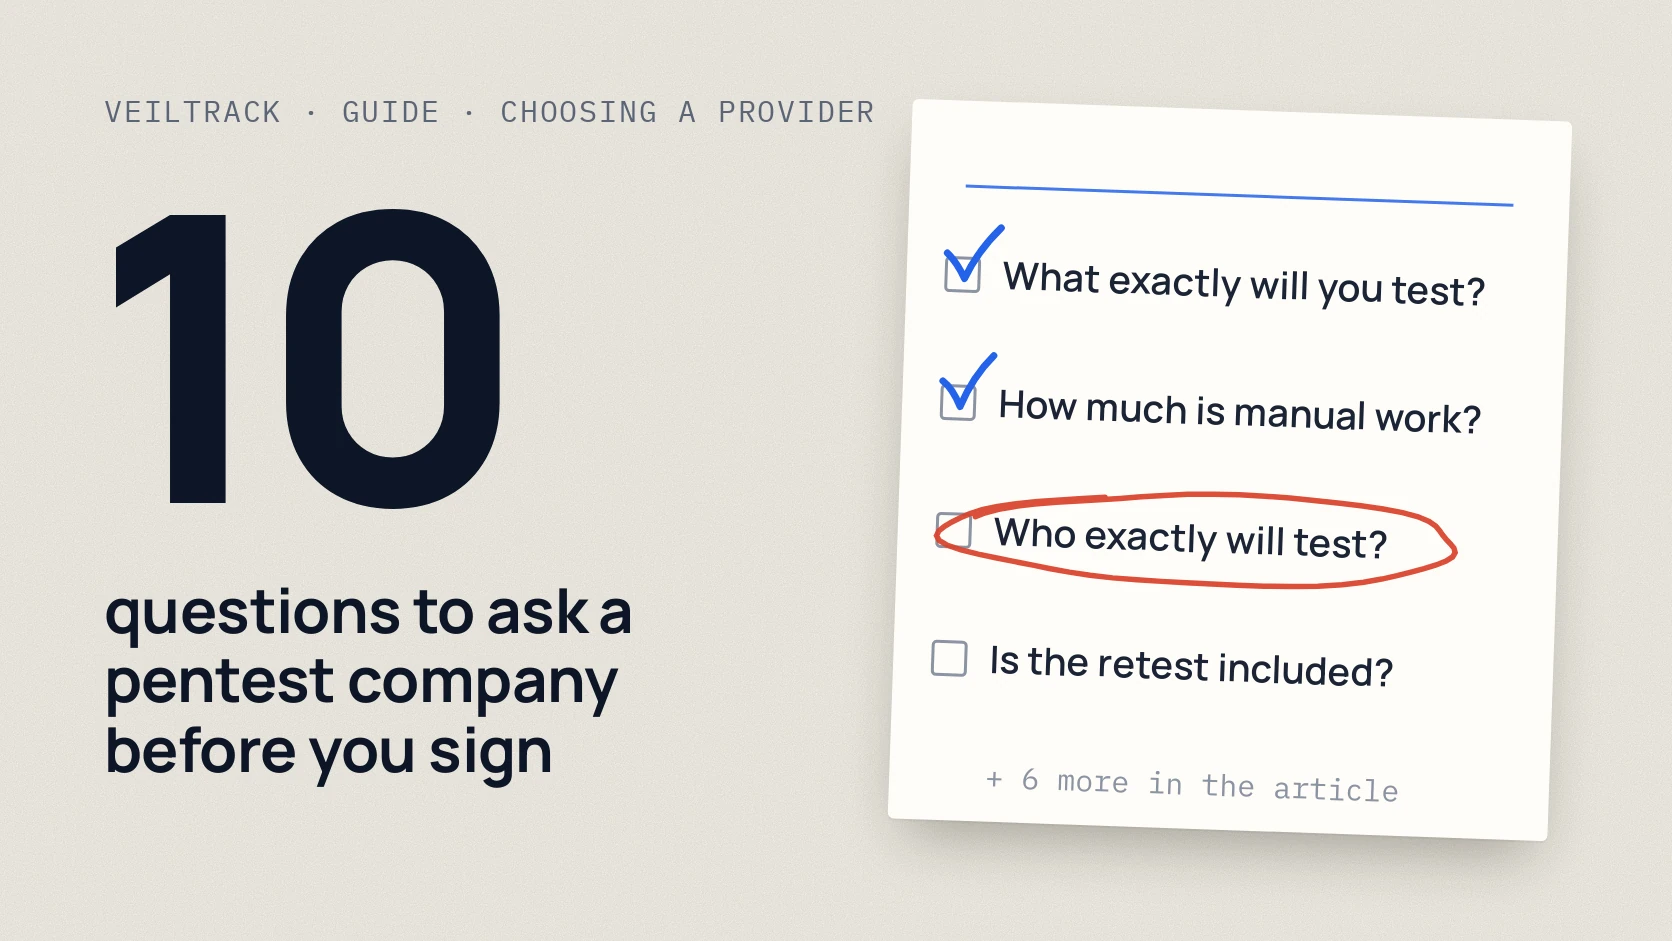
How to choose a pentest provider: 10 questions to ask, red flags, and what the contract and report should include. A checklist for owners and IT.
What a pentest costs in Ukraine and what drives the price: three scope examples in working days, a table of price factors, a checklist and provider choice.